Get phone and SMS alerts fromMicrosoft Sentinel
Microsoft Sentinel is Azure's cloud-native SIEM and SOAR, correlating signals into security incidents. Spike turns every Sentinel incident into an on-call incident and pages the engineer by phone, SMS, Slack, or email until someone acknowledges it, escalating when nobody does.
Set up with AI
I use Microsoft Sentinel for monitoring and Spike for on-call and incident management. Walk me through connecting them: create a Microsoft Sentinel integration in Spike, copy its webhook URL, and add that webhook to Microsoft Sentinel alert settings. Then help me send a test alert to confirm incidents show up in Spike.
What is Microsoft Sentinel?
Microsoft Sentinel collects security data across Azure, Microsoft 365, and other clouds and on-premises systems, and groups the resulting alerts into incidents with a severity and status for the security team to triage.
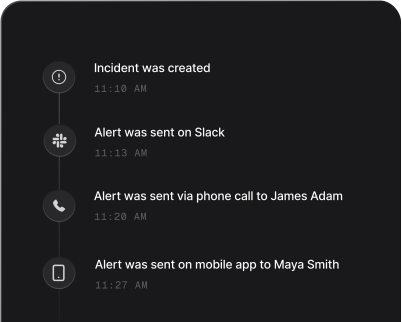
Those incidents wait in the Sentinel queue until someone opens the portal. Sent to Spike through a Logic App playbook, each one becomes an incident that calls and texts the engineer on rotation, escalates to the next responder when it goes unacknowledged, and groups repeat updates to the same Sentinel incident into a single thread instead of a pile of pages.
Severity filtering stays on the Sentinel side, in the automation rule, so a team that only wants to be woken for High severity incidents can route the rest elsewhere.
How to set up Microsoft Sentinel alerts
Every Spike integration is a unique webhook URL. Paste it into Microsoft Sentinel and alerts start flowing — no agents, no code.
Step 1: Create a Microsoft Sentinel integration in Spike
In your Spike dashboard, open Integrations and choose Microsoft Sentinel. Spike generates a unique webhook URL for this integration — copy it.
Step 2: Create a playbook in Sentinel
In Microsoft Sentinel, open Automation and create a playbook (an Azure Logic App) with the Microsoft Sentinel incident trigger. Add an HTTP action that sends a POST to the Spike webhook URL, with the incident details as the JSON body.
Step 3: Run the playbook from an automation rule and test
Create two automation rules that run the playbook, both filtered to the severities you want paged: one on "When incident is created", and one on "When incident is updated" with the condition Status Changed, so closing the incident in Sentinel resolves it in Spike. Generate a test incident to confirm it opens an incident in Spike.
That's it — Microsoft Sentinel alerts now page whoever is on call.