Get phone and SMS alerts fromPort
Port is an internal developer portal that tracks your services, environments, and scorecards. Spike turns a Port automation into an incident and pages the on-call engineer when an entity degrades, then closes it when a second automation reports the recovery.
Set up with AI
I use Port for monitoring and Spike for on-call and incident management. Walk me through connecting them: create a Port integration in Spike, copy its webhook URL, and add that webhook to Port alert settings. Then help me send a test alert to confirm incidents show up in Spike.
What is Port?
Port is an internal developer portal where engineering teams catalogue services, environments, and the scorecards that say whether each one meets your standards. Its automations react when an entity changes and can call a webhook.
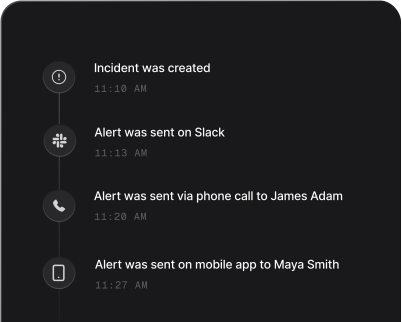
Pointed at Spike, an automation becomes an incident: the on-call engineer is called or texted, handed to the next tier when no one acknowledges, and repeat deliveries for the same alert join the open incident instead of paging again. Each automation carries an alert_id that you define, so a second automation reporting the recovery with status “resolved” closes the same incident without anyone touching it.
How to set up Port alerts
Every Spike integration is a unique webhook URL. Paste it into Port and alerts start flowing — no agents, no code.
Step 1: Create a Port integration in Spike
In your Spike dashboard, open Integrations and choose Port. Spike generates a unique webhook URL for this integration — copy it.
Step 2: Create a firing automation in Port
In Port, add an automation whose condition detects the degradation, with a webhook backend pointing at the Spike URL. Send a JSON body with status "firing", an alert_id built from the blueprint and entity identifiers, and a summary sentence.
Step 3: Create a resolved automation and test
Add a second automation that detects the recovery and sends the same alert_id with status "resolved". Trigger a change on an entity to see the incident open, then recover it to see the incident close.
That's it — Port alerts now page whoever is on call.