Get phone and SMS alerts fromThreat Stack
Threat Stack raises the alarm — Spike.sh makes sure a human hears it. Every Threat Stack alert becomes an incident with on-call schedules, escalations, and alerts on phone, SMS, Slack, email, WhatsApp, and Teams.
Set up with AI
I use Threat Stack for monitoring and Spike.sh for on-call and incident management. Walk me through connecting them: create a Threat Stack integration in Spike.sh, copy its webhook URL, and add that webhook to Threat Stack alert settings. Then help me send a test alert to confirm incidents show up in Spike.sh.
What is Threat Stack?
Threat Stack keeps watch over your systems and raises an alert the moment something goes wrong — a failed check, an error spike, a service that stops responding.
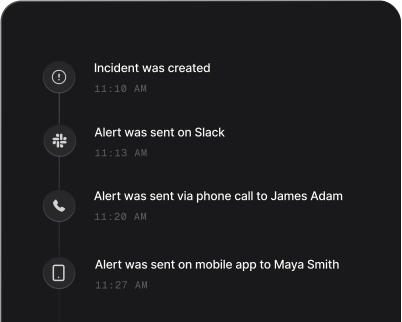
Connected to Spike.sh, those alerts become incidents: the right on-call person gets a phone call and SMS within seconds, similar incidents are grouped to cut the noise, and everything is tracked until it is resolved.
How to set up Threat Stack alerts
Every Spike.sh integration is a unique webhook URL. Paste it into Threat Stack and alerts start flowing — no agents, no code.
Step 1: Create a Threat Stack integration in Spike.sh
In your Spike.sh dashboard, open Integrations and choose Threat Stack. Spike.sh generates a unique webhook URL for this integration — copy it.
Step 2: Add the webhook in Threat Stack
Open the alert or notification settings in Threat Stack, add a webhook endpoint, and paste your Spike.sh webhook URL.
Step 3: Send a test alert
Trigger a test from Threat Stack. The alert lands in Spike.sh as an incident and your on-call team is alerted immediately.
That's it — Threat Stack alerts now page whoever is on call.